
Vulnerability in DNS Servers Discovered By Academics from Israel


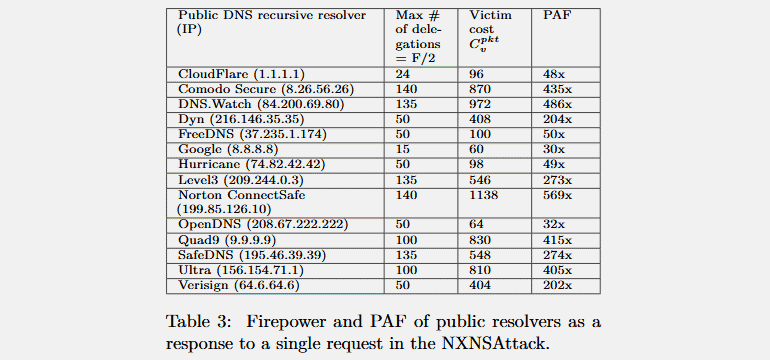
A vulnerability in DNS servers that can be exploited to launch DDoS attacks of huge extents was as of late discovered by a team academics from Israel, the attack as indicated by them impacts recursive DNS servers and the procedure of DNS delegation.

In a research paper published, the academics from the Tel Aviv University and The Interdisciplinary Center in Herzliya, Israel, said they figured out how to abuse this delegation procedure for DDoS attacks. 

The NXNSAttack technique has various aspects and varieties, yet the fundamental steps are detailed below:

1) The attacker sends a DNS query to a recursive DNS server. The solicitation is for a domain like "attacker.com," which is overseen through an attacker-controlled authoritative DNS server. 

2) Since the recursive DNS server isn't approved to resolve this domain, it forwards the operation to the attacker's malicious authoritative DNS server. 

3) The malignant DNS server answers to the recursive DNS server with a message that likens to “I’m delegating this DNS resolving operation to this large list of name servers." The list contains a large number of subdomains for a victim website.

4) The recursive DNS server forwards the DNS inquiry to all the subdomains on the list, giving rise to a surge in traffic for the victim's authoritative DNS server.


The Israeli researchers said they've been working for the past few months with the producers of DNS software; content delivery networks, and oversaw DNS suppliers apply mitigations to DNS servers over the world. 

Affected software incorporates the likes of ISC BIND (CVE-2020-8616), NLnet labs Unbound (CVE-2020-12662), PowerDNS (CVE-2020-10995), and CZ.NIC Knot Resolver (CVE-2020-12667), yet additionally commercial DNS administrations provided by organizations like Cloudflare, Google, Amazon, Microsoft, Oracle (DYN), Verisign, IBM Quad9, and ICANN.


Patches have been discharged over the previous weeks. They incorporate mitigations that keep attackers from mishandling the DNS delegation procedure to flood different DNS servers.

The research team's work has been properly detailed in a scholarly paper entitled "NXNSAttack: Recursive DNS Inefficiencies and Vulnerabilities," available for download in PDF format.


source https://www.ehackingnews.com/2020/05/vulnerability-in-dns-servers-discovered.html

Comments

Popular posts from this blog

Betting and Gambling Websites under Cyberattack from Chinese Hackers

Since last year's summers, Chinese hackers have been targeting South Asian companies that own online gambling and betting websites. The gambling companies in South Asia have confirmed the hacks, whereas rumors of cyberattacks on betting websites have also emerged from Europe, and the Middle East, however, the rumors are yet to confirm, says the reports of cybersecurity group Trend Micro and Talent-Jump. Cybersecurity experts claim that no money was stolen in these hacks against the gambling websites. However, hackers have stolen source codes and databases. The motive of the attack was not a cybercrime, but rather espionage intended attack to gain intelligence. According to the experts, a group named ' DRBControl ' is responsible for the cyberattack. According to the reports of Trend Micro, the hacking techniques used in this particular cyberattack incident is similar to methods done by Emissary Panda and Winnti. All of these hacking groups are from China that has launc...

Github Escapes from Octopus Malware that Affected its 26 Software Projects

Github, a platform where every malicious software report is equally different in its place, manages to escape from a malware threat.  Github, an organization that united the world's largest community of coders and software developers, revealed that hackers exploited an open-source platform on its website to distribute malware. The hackers used a unique hacking tool that enabled backdoors in each software project, which the hackers used to infiltrate the software systems. "While we have seen many cases where the software supply chain was compromised by hijacking developer credentials or typosquatting popular package names, a malware that abuses the build process and its resulting artifacts to spread is both interesting and concerning for multiple reasons," said Github on its security blog. Fortunately, the hackers attempt to exploit the open-source platform was unsuccessful. Still, if it were, on the contrary, hackers could've secured a position in the softwares, ...

Maze Ransomware Operators Leaked 2GB of Financial Data from Bank of Costa Rica (BCR)

Bank of Costa Rica (BCR) has been receiving threats from the threat actors behind Maze ransomware who have stolen credit card details from the bank, the ransomware gang started publishing the encrypted financial details this week. The Banco de Costa Rica is one of the strongest state-owned commercial banks operated in Costa Rica, starting from humble origins of mainly being a private commercial bank, it expanded to become a currency issuer and one of the most renowned baking firms in Central America contributing largely in the financial development of the nation. The hacker group behind the data leak have demanded a ransom from Banco de Costa Rica at various occasions, however, to their dismay they observed a lack of seriousness in the way the bank dealt with these previous leaks and it served as a primary reason that motivated the latest data leak, according to an interview with Maze ransomware operators. As per the claims made by the attackers, Banco de Costa Rica's netw...